It’s amazing the number of people I come across who are still using an unsecured spreadsheet to keep track of passwords. I understand how it happens. Someone needed a place to write down the login for the copier, then the bank, then the website, and a spreadsheet was already open. Years later it has two hundred rows, three people know where it lives, and nobody is quite sure who else has a copy.
I have been doing this work for a long time, and I would rather not lecture anyone about it. A spreadsheet felt organized, and in a way it was. The trouble is that it does almost nothing to protect what it holds. Anyone who opens the file sees everything. It gets emailed, synced, backed up and copied to a laptop that later walks out the door. When someone leaves, there is no clean way to take their access away short of changing every password on the list, which nobody ever has time to do.
Passwords saved in a web browser are a step up, but only a small one. They tend to be tied to one person’s account on one device, they are hard to share properly with a coworker, and they are easy to lose track of when that person moves on.
What a password manager does instead
A password manager is a locked vault for logins. Each person has their own account, protected by one strong passphrase they actually remember. The manager creates long, random passwords for everything else, fills them in for you, and keeps them encrypted, so the company running the service cannot read them either.
For an office, the useful part is sharing. You set up shared vaults by role. The front desk gets the vendor portals it needs, the bookkeeper gets the bank, and the board treasurer gets what the treasurer needs. When someone leaves, you remove their account, and their access to the shared logins goes with it. Nothing has to be retyped or emailed around.
There are several good options. Bitwarden, 1Password and Proton Pass are three well-known ones, and each has plans for small teams. They differ in price, interface and where they keep your data, and the right one depends on how your organization already works. I am not paid by any of them, and I will tell you plainly if the one you are already using is fine.
Passwords and second factors in one place
The bigger change in the last few years is that many password managers now handle more than passwords.
Most can store the six-digit authenticator codes that sites ask for after your password, the second step in multi-factor authentication (MFA). Instead of a separate phone app that only one person can see, the code lives next to the login it belongs to, and it can be shared with the people who need it.
Many also support passkeys. A passkey is a newer kind of sign-in, built on the same FIDO2 standard as hardware security keys, that replaces the password altogether. There is nothing to type, and it is very hard to phish, because a passkey only works on the real site it was made for. The password manager can store passkeys and sync them across your devices.
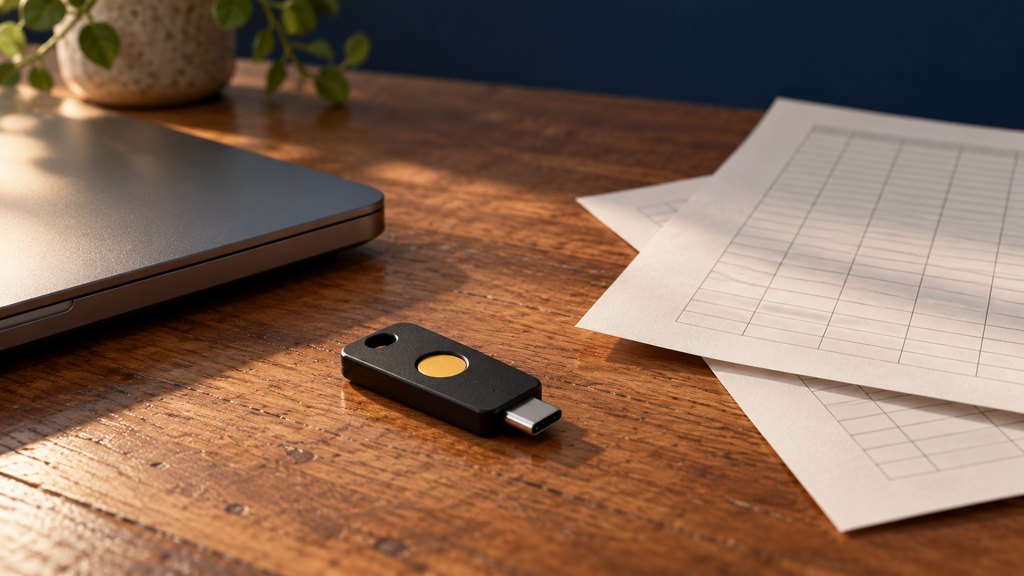
And the password manager itself can be protected with a hardware security key, a small device that plugs into a USB port or taps against a phone. Someone who learns a staff member’s passphrase still cannot get into the vault without the key in hand.
One tool covering passwords, codes and passkeys is simpler to run, and simpler is what gets used. For your most important accounts, such as the password manager itself, email and banking, I still recommend a second factor that lives outside the vault. That way a single mistake cannot open everything at once.
What I do
For small businesses and nonprofits, I set this up from start to finish:
- Choose the tool with you. We pick one that fits your budget, your devices and how your people work.
- Move everyone off the spreadsheet. I bring in the existing passwords, retire the spreadsheet and the browser-saved logins, and change the ones that were exposed along the way.
- Turn on MFA. That covers the password manager itself and every important account that supports it, with hardware security keys for the people and accounts that need them most.
- Set up shared vaults. Each one is organized by role, so people see what they need and nothing else.
- Plan for emergencies. We decide who can get in if the person who holds the keys is out sick, on vacation or gone, and we write it down and test it.
- Train your staff. I show people how to use it in plain language, in short sessions, at a pace that suits a busy office.
When we are done, you own the account and the vault, in your organization’s name. I don’t keep a copy of your passwords, and you are never tied to me to keep it running.
Getting started
If your passwords live in a spreadsheet, a notebook or someone’s browser, this is one of the most useful things you can do for your organization’s security. Every office is different, so I quote after a short conversation about what you use now and who needs access to what. Contact DataStream Consulting for a quote, and I will reply personally.
Practical IT. Personal service.